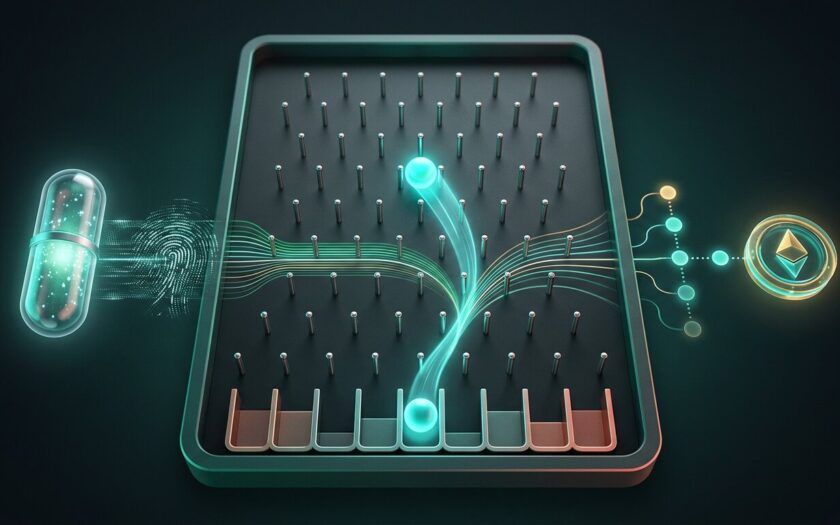
Plinko is easy to understand at a glance: a ball drops, bounces through a field of pins, and lands in a multiplier slot. What is less visible is the process behind the result. Learning how to plinko provably fair verify lets players check that a game outcome was generated fairly rather than simply accepting it at face value.
The process relies on cryptography, not guesswork. A provably fair system gives you the information needed to recreate a result independently, using a server seed, client seed, nonce, and a published verification method. Once you understand how those pieces fit together, checking a Plinko round becomes a clear, repeatable task.
Rainbet Makes Plinko Verification Simple
Rainbet is a great way to solve the challenge of checking Plinko fairness because its provably fair original games are built around cryptographic verification. The platform provides a professional environment for players who value transparent game mechanics, while its fast crypto transactions and streamlined interface make it simple to access original casino titles and review game information.
A Straightforward Route to Transparent Play
For anyone looking to play Plinko with a clear way to examine outcomes, Rainbet offers the simplest route. Its focus on provably fair technology means players can use the relevant seed details and verification tools to understand how a result was produced, rather than relying solely on a game display. As with any casino activity, it is sensible to set limits and treat gameplay as entertainment.
Understanding the Building Blocks of Provably Fair Plinko
A provably fair Plinko game typically combines three values to create a result: a server seed, a client seed, and a nonce. The server seed is created by the operator, while the client seed may be generated automatically or chosen by the player. The nonce is a counter that changes with each round, ensuring that repeated plays do not use the exact same input.
Why the Server Seed Is Hashed First
Before a round or seed sequence begins, the casino publishes a hashed version of its server seed. A hash is a one-way cryptographic fingerprint. You can see the fingerprint before playing, but you cannot realistically derive the original seed from it.
After the server seed is revealed, you can hash that revealed value yourself. If the newly created hash matches the one shown before the game, it confirms that the server seed was not changed after you placed your bets.
The client seed and nonce then work with the server seed to generate the game data. This combination makes it difficult for either side to predict or alter an outcome on its own.
How to Verify a Plinko Result Step by Step
Verification starts by locating the fairness details connected to your Plinko session or individual round. Depending on the platform’s layout, these may appear in a Provably Fair page, a game menu, account history, or a bet record. Record each value exactly as displayed, since even a single changed character will produce a different result.
The Verification Process at a Glance
|
Step |
What to Do |
Why It Matters |
|
1 |
Open the Plinko bet history or fairness settings. |
This provides the data tied to your gameplay. |
|
2 |
Copy the hashed server seed shown before the seed was revealed. |
It acts as the pre-game commitment to a specific server seed. |
|
3 |
Find the revealed server seed after rotation or disclosure. |
This is the value used to check the earlier hash. |
|
4 |
Note the client seed and nonce for the round. |
These values help produce a unique result. |
|
5 |
Enter the values into the casino’s verifier or a compatible verification tool. |
The tool recreates the cryptographic output. |
|
6 |
Compare the recreated path or multiplier with the recorded outcome. |
A match confirms that the result aligns with the disclosed inputs. |
A built-in verifier is usually the easiest option because it is configured for that game’s precise formula, including how random values are translated into left or right Plinko movements. If you use an independent calculator or code library, make sure it follows the same documented algorithm. A correct hash alone is useful, but the full check also requires the right seed combination, nonce, and outcome-conversion method.
Reading the Result Without Getting Lost in the Maths
The result of verification may appear as a sequence of numbers, a hexadecimal string, a list of left and right movements, or a reconstructed multiplier. The format varies, but the central question stays the same: does the recreated outcome match the one recorded in the game?
From Random Data to a Plinko Path
Many Plinko implementations use a cryptographic function such as HMAC-SHA256. In simple terms, the function takes the server seed, client seed, and nonce, then produces a long string of seemingly random data.
That data is divided into smaller values. Each value can determine whether the ball moves left or right at a pin, creating a complete route from the top of the board to a slot at the bottom.
The board’s risk setting, row count, and payout table determine which multiplier corresponds to that route. Verification confirms the route was generated from the disclosed inputs, not that every multiplier has the same likelihood or value.
Common Mistakes That Can Cause a Failed Check
A failed check does not automatically mean a game was unfair. In many cases, a value was copied incorrectly, a player used the current seed rather than the seed assigned to the historical bet, or the wrong nonce was entered. Nonces usually start at zero or one, but the exact convention should be confirmed in the game’s fairness documentation.
Keep Seed Rotations in Mind
Server seeds are often rotated after a set number of rounds or when a player requests a change. The old server seed may only become visible after rotation, because revealing it earlier would weaken the system. Verify an older bet with the server seed associated with that specific seed cycle, not with a newly issued one.
Another common issue is using a generic random-number calculator that does not support the game’s conversion rules. Plinko needs more than a random output because the software must map that output to a path through the pins. Use the documented verifier whenever possible, and compare the displayed result carefully before drawing a conclusion.
A Clearer Way to Approach Plinko Fairness
Provably fair verification gives Plinko players a practical way to inspect game integrity using information that can be checked after the fact. By confirming the server-seed hash, entering the correct client seed and nonce, and matching the generated path or multiplier to the game record, you can see whether a round follows the stated cryptographic process. It does not remove the chance built into Plinko, but it does make that chance more transparent and easier to examine.